Details
-
Bug
-
Status: Needs Feedback (View Workflow)
-
 Critical
-
Resolution: Unresolved
-
11.8.8
-
None
-
Operating System: Windows Server
MariaDB Version: 11.8.8
Test Interfaces: Adminer web interface + MySQL CLI
Database Client: MySQL command line client
Test Account: csv_db_loader@localhost
Reproduction Method: Tested CREATE/DROP DATABASE commands from both Adminer UI and command line
Status: Bug confirmed - account can CREATE and DROP databases despite having no global CREATE privilegeOperating System: Windows Server MariaDB Version: 11.8.8 Test Interfaces: Adminer web interface + MySQL CLI Database Client: MySQL command line client Test Account: csv_db_loader@localhost Reproduction Method: Tested CREATE/DROP DATABASE commands from both Adminer UI and command line Status: Bug confirmed - account can CREATE and DROP databases despite having no global CREATE privilege
-
Can result in data loss
Description
ISSUE: MariaDB 11.8.8 - Privilege Escalation: Table-level privileges grant unintended global CREATE/DROP capabilities
SEVERITY: Critical - Data Loss Risk
DESCRIPTION:
An account created with ONLY table-level privileges (SELECT, INSERT, UPDATE, DELETE) on specific databases can execute global database operations (CREATE DATABASE, DROP DATABASE). This is a serious privilege escalation vulnerability.
STEPS TO REPRODUCE:
1. Create account with table-level privileges only:
CREATE USER 'test_user'@'localhost' IDENTIFIED BY 'password';
GRANT SELECT, INSERT, UPDATE, DELETE ON db_1.* TO 'test_user'@'localhost';
GRANT SELECT, INSERT, UPDATE, DELETE ON db_2.* TO 'test_user'@'localhost';
GRANT SELECT, INSERT, UPDATE, DELETE ON db_3.* TO 'test_user'@'localhost';
FLUSH PRIVILEGES;
2. Verify account privileges:
SHOW GRANTS FOR 'test_user'@'localhost';
Result: Shows ONLY table-level grants - no global CREATE privilege
3. Connect as test_user and execute:
CREATE DATABASE test_privilege_bug;
4. Verify database was created:
SHOW DATABASES;
5. Verify account can also drop databases:
DROP DATABASE test_privilege_bug;
6. Verify database was dropped:
SHOW DATABASES;
EXPECTED BEHAVIOR:
- SHOW GRANTS should show only: SELECT, INSERT, UPDATE, DELETE on db_1., db_2., db_3.*
- CREATE DATABASE should fail with: "Access denied for user 'test_user'@'localhost' to database 'test_privilege_bug'"
- DROP DATABASE should fail with: "Access denied for user 'test_user'@'localhost' to database 'test_privilege_bug'"
ACTUAL BEHAVIOR:
- Account successfully creates databases (bug!)
- Account successfully drops databases (bug!)
- Global CREATE/DROP operations are permitted despite no global privileges granted
TESTED INTERFACES:
- Adminer web interface: Bug confirmed
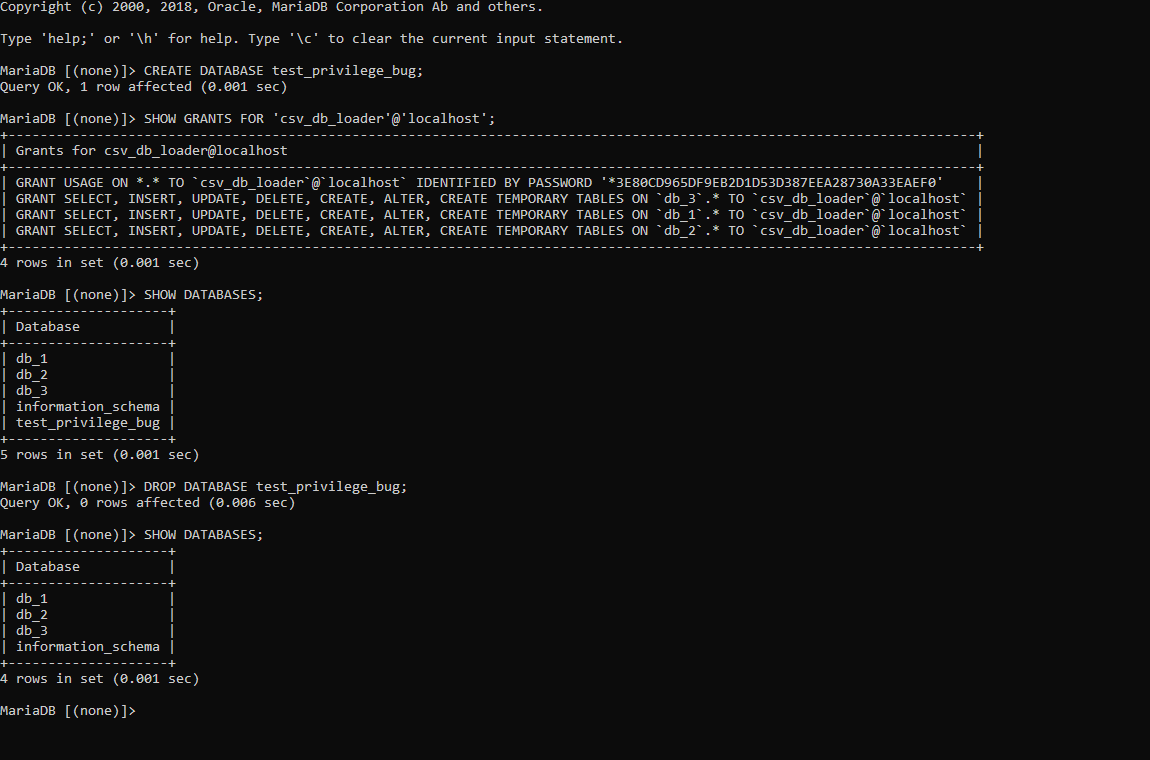
- MySQL CLI: Bug confirmed (see attached screenshot)
SECURITY IMPACT:
- Privilege isolation is broken
- Service accounts can escalate privileges beyond intended scope
- Databases can be deleted causing complete data loss
- Violates principle of least privilege
- Critical for multi-tenant or secure deployments
ROOT CAUSE:
Table-level GRANT appears to implicitly grant global CREATE/DROP privileges, contrary to MariaDB documentation and expected behavior.
ENVIRONMENT:
- Operating System: Windows Server
- MariaDB Version: 11.8.8
- Test Method: MySQL CLI + Adminer web interface
- Tested Account: csv_db_loader@localhost with table-level grants only
EVIDENCE:
See attached screenshot showing:
1. Account privileges (table-level only)
2. Successful CREATE DATABASE (should fail)
3. Database listed in SHOW DATABASES
4. Successful DROP DATABASE (should fail)
5. Database removed from SHOW DATABASES
WORKAROUND ATTEMPTED:
Host-based restrictions (localhost only) do NOT prevent this bug.
REQUESTED ACTION:
1. Confirm if this is expected behavior in MariaDB 11.8.8
2. If bug: Provide fix to enforce table-level privilege scope
3. If design limitation: Document security implications and recommend workarounds